Online Poker's New Security Threat Emerges: Compromised 3rd Party Tools

pessi-lamm
37 minutes ago
Pessi Lamm 37 minutes ago
Share this article
Or copy link
  • Attackers allegedly used compromised 3rd-party poker tools to watch high-stakes players’ screens for an entire year.
  • Trusted tools like Jurojin and IntuitiveTables got hit, while the poker rooms themselves apparently stayed out of it.
  • And the nasty bit? Everyone sitting across the table from a compromised player could potentially be a victim too.
The RAT was on the PC, but the whole table could be in trouble.
Online poker's clanker-licking 3rd party software users have a new problem, and it’s potentially threatening everybody at the table.

A security investigation has uncovered what appears to be a highly targeted operation against high-stakes players, where a remote-access agent/tool was allegedly delivered to their computers through compromised 3rd party poker software.

Its capabilities? To see what’s happening on the infected players' screens. Yes, hole cards, everything.

The current estimate is around 30 affected players across Europe, North America and Oceania.

One of the unfortunate software makers involved, Jurojin, has since confirmed that compromised versions of its software were delivered to a specific group of users, while another software maker, IntuitiveTables, has also confirmed it was targeted.

That sounds like a story about 30 unlucky high rollers, but it’s bigger than that.

And Before Everyone Starts Blaming The Poker Rooms...

So far, no poker site's own software has been identified as compromised. GGPoker, ClubWPT Gold, WPN/ACR, CoinPoker and WPT Global have all been specifically reported as not involved in the attack.

The attack appears to have come through the side door instead, via third-party poker software running on the players' computers.

Meet the New Potential Online Poker Security Threa

If you've spent enough time playing serious online volume, Jurojin and IntuitiveTables won't exactly sound like exotic software.

Jurojin handles table management, tiling, hotkeys, betting tools and HUD-style information. IntuitiveTables operates in much the same neighbourhood, with table placement, hotkeys, bet sizing and overlays.

Useful stuff when you're trying to operate a high-functioning online poker system from a Windows desktop.

And that's precisely why the latest “RAT” scandal is so nasty.

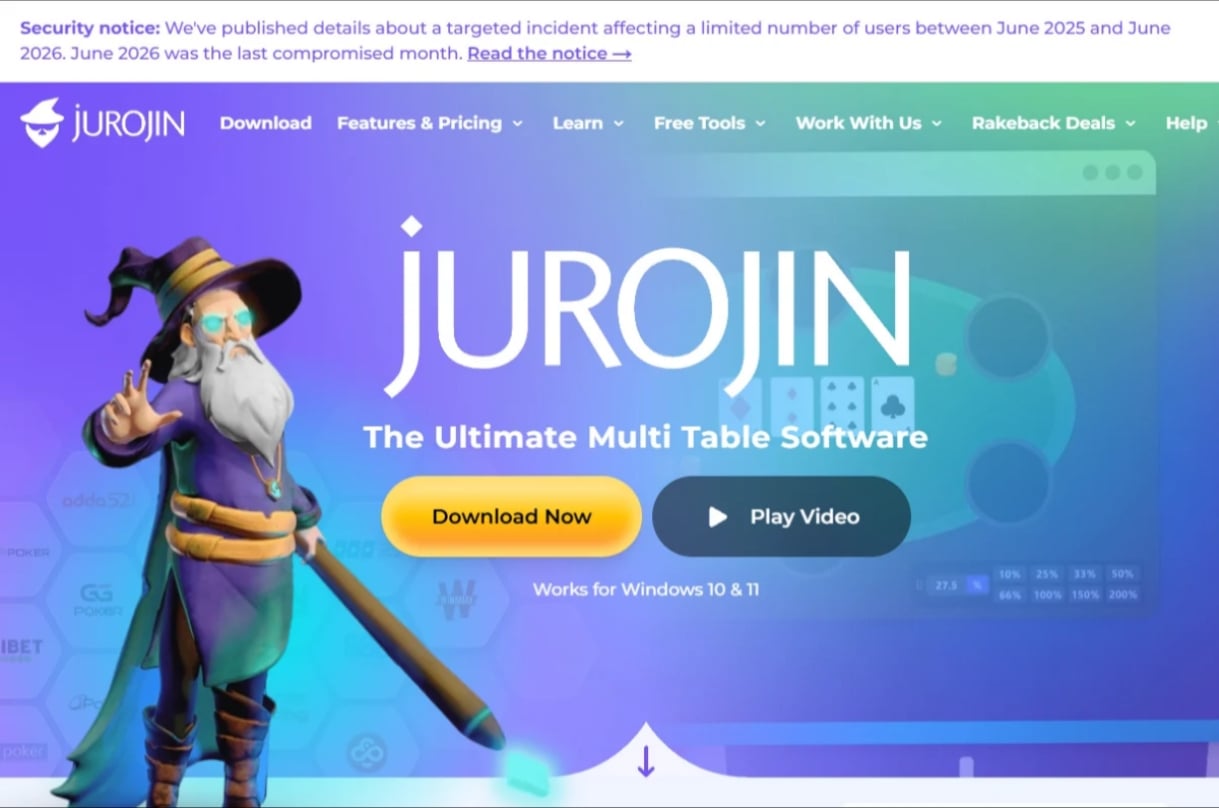
Jurojin
Jurojin homepage with the security notice about the incident.

There Could Be Spy In Your Room

These programs sit right next to the poker client. They interact with the tables, process information from them and, depending on the functionality being used, can control various parts of the player's workflow.

That makes compromised third-party software a potential online poker security threat to the whole table, not just the infected clanker-licker.

Think of it like someone bringing a spy tool into a room where important decisions are being made... not cool.

Somebody Was Apparently Watching Via Mesh Agent and MeshCentral

The remote-access component has been identified as Mesh Agent, part of MeshCentral, a legit open-source remote-management platform. The software itself isn't malware. It’s a tool that can be used to manage a computer remotely.

According to the cybersecurity researcher behind the investigation, the agent could allow remote screen viewing, mouse and keyboard control, running commands with system-level privileges, and access to files on the computer.

The screen access is the particularly ugly bit for poker players. If you're sitting there playing high stakes, your hole cards are right there on the screen.

Jurojin Confirms It’s Time to Get Paranoid

Jurojin has confirmed that an attacker intermittently replaced update packages delivered to a specific group of users between June 2025 and June 2026.

Some of those tampered packages contained a remote-access tool (RAT). Jurojin says June 2026 was the final month in which a compromised update was delivered, and says it has logs showing the affected versions and users.

Are you telling me this went on for a year?

IntuitiveTables has separately confirmed that a known cheater targeted several applications in an attempt to install spyware on specific high-stakes players, and says its current public versions have been checked and contain no malicious code.

So, Are Third-Party Tools The Problem?

Not automatically, but they are clearly a potential security threat.

Online poker has gradually built an ecosystem around the poker client. Table managers, HUDs, trackers, RTAs, hotkey tools and various other bits of grinder machinery have become completely normal.

The problem is trust.

If the software can see what's happening on your screen, a compromised version can potentially let someone else see it too.

Now we have a real-world example of what can happen when that trust is compromised.

The 30 Players Aren't The Whole Story

So what happened here? Someone infiltrated a critical supply line and targeted the weak links, who in this case happened to be 3rd party poker tool users. After that, it was just popcorn time and figuring out how to maximize the profits.

I refuse to see these 30 players as the only victims.

The player whose PC gets compromised is obviously in trouble. But if an attacker can see that player's cards while they're playing, the problem doesn't stop at the infected machine.

There are other players sitting at the table.

They don't need to have the malware. They don't need to have installed Jurojin. They don't even need to know anything is happening.

They just need to be there at the same table.

We don't have a complete list of affected tables or hands, so there is no sensible way to calculate the damage yet.

But this is clearly bigger than "30 high-stakes players got hacked."

More Poker News

Upcoming Events